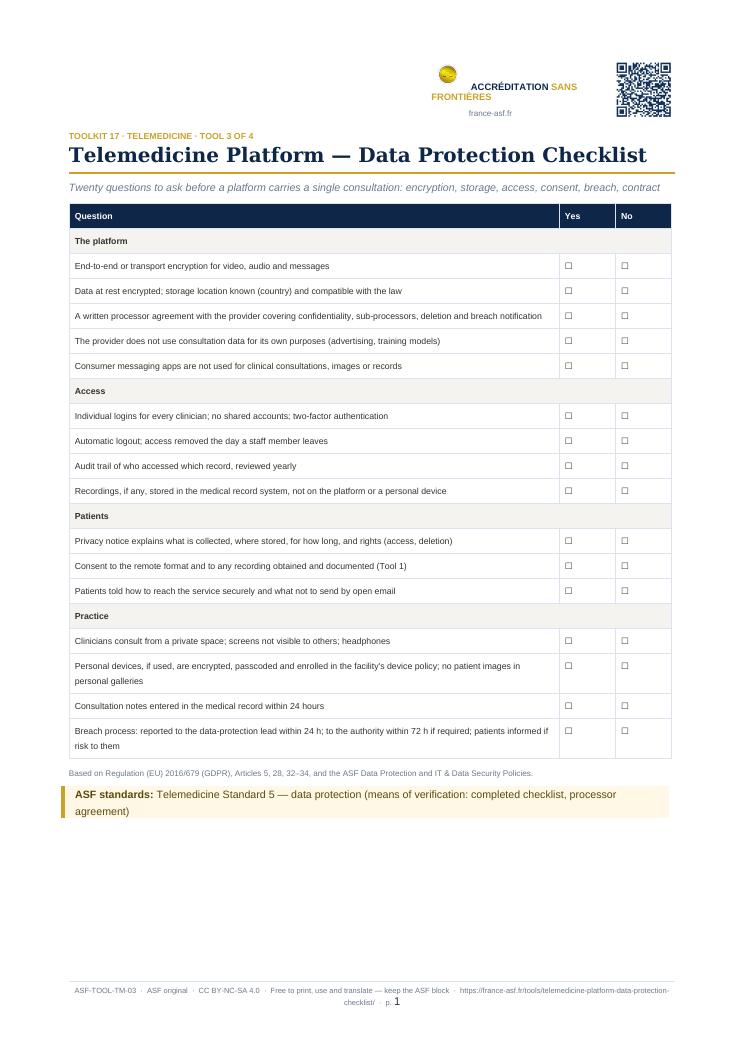
Telemedicine Platform — Data Protection Checklist
Twenty questions to ask before a platform carries a single consultation: encryption, storage, access, consent, breach, contract
What it is
A GDPR-aligned checklist for choosing and running a telemedicine platform: encryption in transit and at rest, where data is stored, who can access recordings and messages, logins and audit trail, consent and recording rules, breach process, the processor contract, and staff practice on personal devices.
Where to use it
Data-protection lead and the clinical lead before adopting a platform; reviewed yearly. Evidence for: Telemedicine Standard 5 — data protection; ASF Data Protection Policy; IT & Data Security Policy. Evidence for: Telemedicine Standard 5 — data protection; ASF Data Protection Policy; IT & Data Security Policy. Evidence for: Telemedicine Standard 5 — data protection; ASF Data Protection Policy; IT & Data Security Policy. Evidence for: Telemedicine Standard 5 — data protection; ASF Data Protection Policy; IT & Data Security Policy.
Translate and adapt
English master edition. Georgian and other translations are added as they are clinically reviewed. Any facility may translate, add its logo and adapt wording to local practice — keeping the ASF block, the source attribution and the licence line on the sheet. Clinical thresholds and drug doses must be confirmed against national protocols before use.
The same code is printed on the tool itself. Scan it in any facility to reach this page.
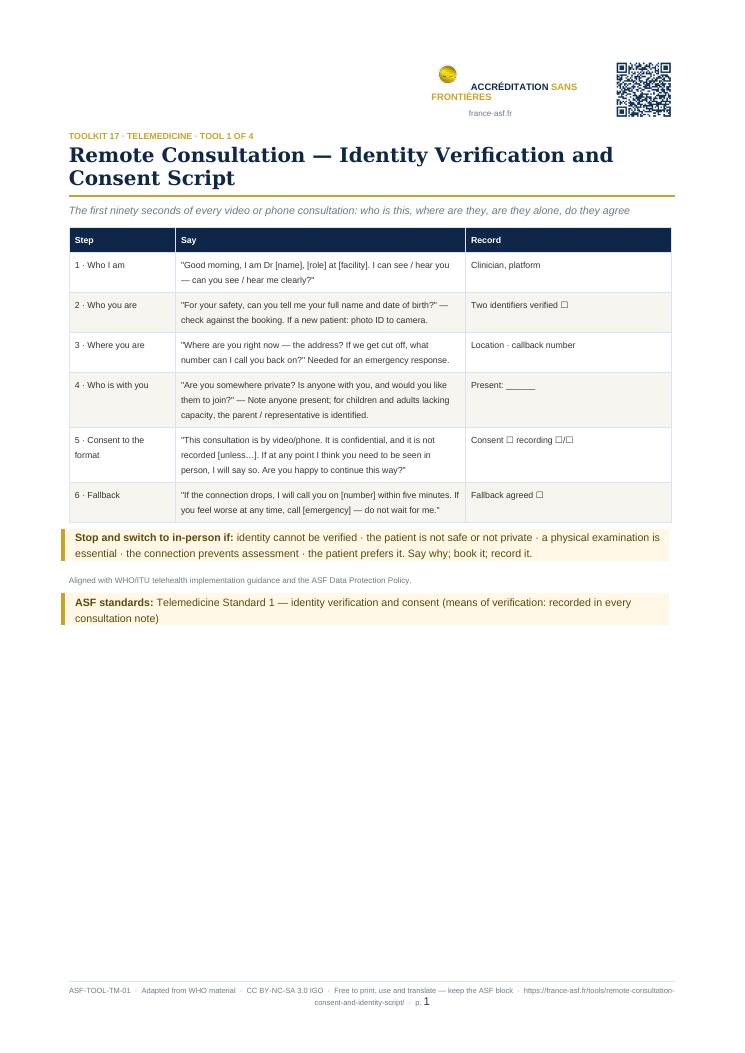 Remote Consultation — Identity Verification and Consent Script
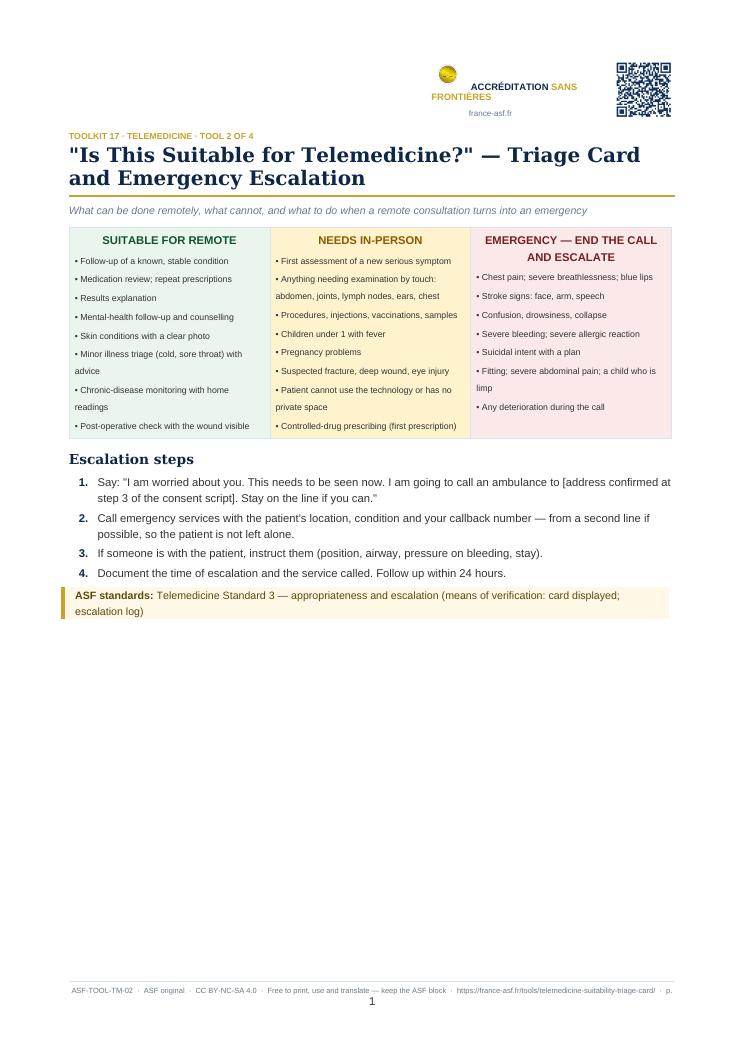 "Is This Suitable for Telemedicine?" — Triage Card and Emergency Escalation
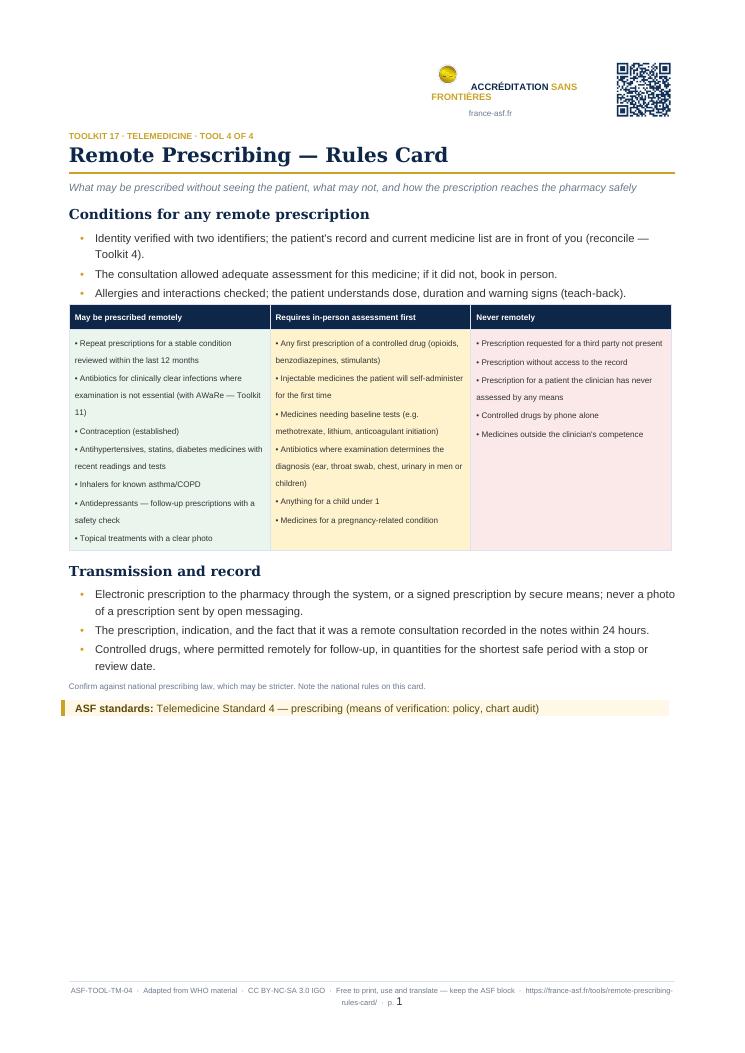 Remote Prescribing — Rules Card
Print to share.